Connect with us

Business

Forecasts, automation and risk management: Machine learning’s impact on the financial sector
Source: Finance Derivative

By Ronald Binkofski, CEO at STX Next

Armed with the capabilities of machine learning (ML), financial institutions and finance executives have long been turning unstructured information into insights that promote better decision-making and help them understand many key elements of the business. Without these insights, financial institutions are less efficient in a number of ways, such as being unable to make fast and accurate decisions on whether to approve a loan or invest in particular assets.

The need to make the very most of AI and ML is clear. According to research from the World Economic Forum, 77% of businesses believe that the two closely related technologies will be essential to their business within the next few years.

Aside from helping make faster business decisions, machine learning algorithms can help financial services companies identify and thwart fraudulent activities and cyber threats, or easily incorporate solutions like chatbots and voice assistants to automate customer service tasks. Such activities, powered by machine learning models, are essential for financial companies to stay ahead of their competitors in as the industry continues its rapid evolution.
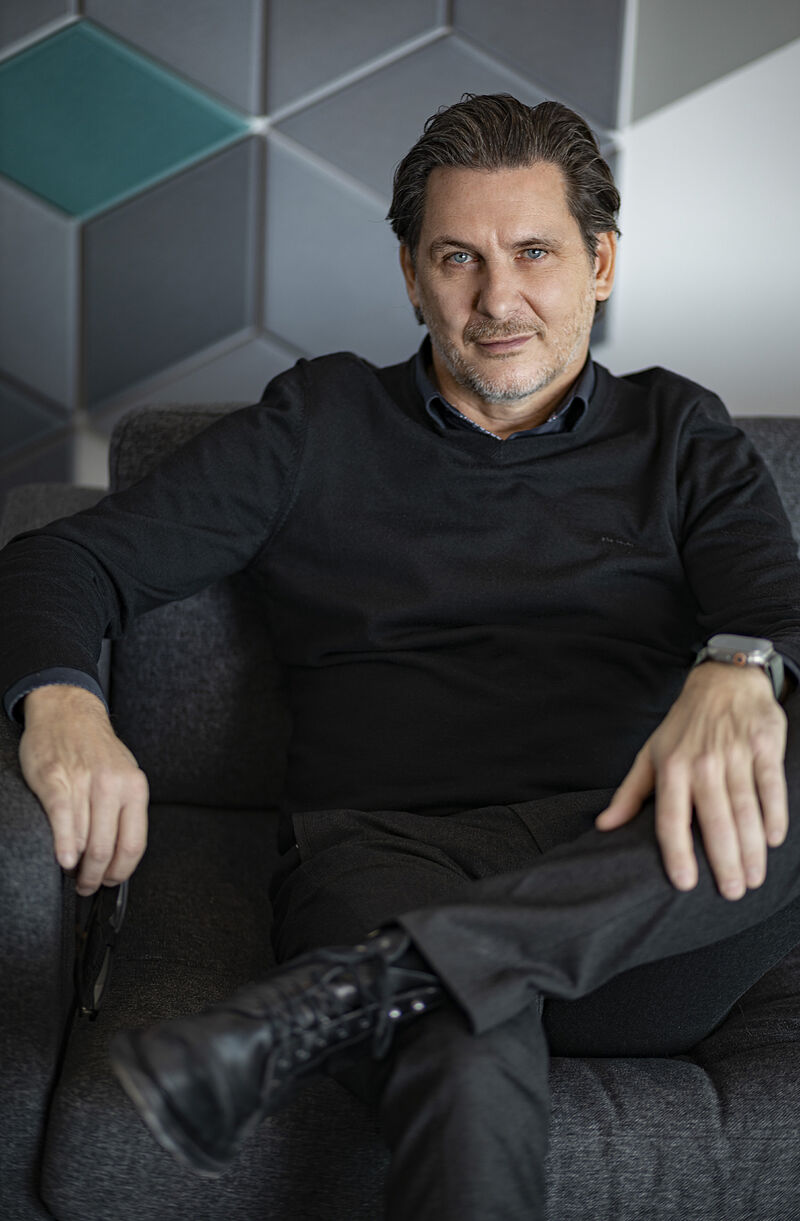
Ronald Binkofski

Processing and analysing raw data to create valuable insights is especially crucial for the following use cases:

Banking and customer service

At a customer-facing level, machine learning helps the banking industry deliver better customer experience and improve operational efficiency. Teams can eliminate manual, repetitive tasks to free up time for strategic work, with machine learning technology offering greater automation, accuracy, and data-driven predictions. Banking institutions can easily detect anomalies in accounting entries by comparing them to other entries for similar transactions.

When it comes to customer service, machine learning-based chatbots and virtual assistants reduce the time customers have to wait before being served. Some of those tools can perform simple tasks like sending notifications, while other AI functions can also manage customer claims, ensuring each of them is handled efficiently and accurately.

Insurance

Machine learning is also an integral part of the creation of new insurance technologies and applications. Paired with automation capabilities, machine learning algorithms can bring improved efficiency in areas such as policy management and financial monitoring. It also supports risk assessment processes, enabling financial companies to analyse vast amounts of financial data and predict risk profiles accurately. With the resulting insights, companies can offer personalised insurance products that cater specifically to the customer’s requirements.

Corporate finance

Machine learning solutions can be widely implemented by data scientists in corporate finance as they are perfect for demand forecasting, as well as anomaly and error detection. This can be used to highlight transactions that have been made in error or potentially violate accounting policies. These models forecast the percentage of completion metrics such as hours, cost, and units, to predict POC revenue and the total completion effort remaining. Algorithms can be also used to forecast when customers will pay invoices, triggering proactive collection efforts before payments are past due.


Risk management and fraud
Banks and financial institutions can use models to determine whether a client would be a good candidate for a loan by using the available financial data to determine if a customer is likely to default on it. Such processes can significantly improve loan application processing efficiency and accuracy. Machine learning automates risk scoring and financial monitoring, which also improves decision-making and increases accuracy in risk and portfolio management in financial markets.


Fraud and abuse are major problems for banking institutions, accounting for billions of dollars in losses each year. ML algorithms can scan through large data sets to detect unique activities or anomalies and flag them to users for further investigation.

Trends, forecasts and predictions
Machine learning also assists in building online applications that provide automated financial advice to investors, making portfolio management seamless and easy. Machine learning can assign categories to transactions affecting customers’ bank accounts, while AI learns how to categorise transactions based on the title of the transfer, its originator, or recipient.

Companies can also use models to automatically predict stock prices. The models are provided with vast amounts of historical data on a company’s stock and then used to extract key trends and essential features that define the stock performance. If the parameters, features, and trends are extracted effectively, the model can accurately predict future stock prices and performance, enabling it to make smart trading decisions.

In the near future, algorithms will have an even more accurate picture of what will work and what won’t, based on the vast amounts of historic data they will possess. AI-powered applications will undoubtedly continue to flood the market, providing more value at a faster pace than traditional approaches.
Continue Reading
Click to comment

Leave a Reply

Your email address will not be published. Required fields are marked *

Business

PSD3 and the Real-Time Fraud Imperative: What the Regulation Actually Demands of Financial Infrastructure 

Baiba Miezere, Group Product Development Director at Eastnets 

The payments industry has spent years treating fraud prevention as a detection problem. PSD3 reframes it as an infrastructure problem, and that distinction matters enormously for how institutions should now be thinking about their technology stack. 

The Regulatory Signal Worth Reading Carefully 

PSD3 is frequently discussed in terms of its compliance burden: stronger authentication, expanded liability, tighter rules around authorised push payment fraud. But the more important signal is structural. By increasing liability for fraud losses and accelerating the shift toward instant payment rails, the regulation is effectively forcing fraud prevention out of the back office and into the transaction execution path itself. While PSD was concentrating more on cards, pull payments, reversible transactions, PSD3 addresses rapidly growing pain-point in financial market: instant payments, irreversible push payments, open banking Account-to-account payments, real time fraud.   

This is a meaningful change. For most institutions, fraud review has historically happened after the fact, a monitoring function that flags anomalies, investigates cases, and seeks recovery. That model was always imperfect, but it was manageable when payment cycles gave you hours or days. Instant payments collapse that window to seconds. Once funds move, recovery options are limited. The liquidation point, where fraudsters convert access into irreversible transfers, now happens faster than most legacy fraud systems can respond. Fraud methods have also rapidly evolved: social engineering scams, synthetic identities, account takeovers, authorised push payment fraud – all requiring shift from traditional post-transaction rule-based monitoring to real-time cross-payment channels detection, combined with behavioural biometrics and artificial intelligence layer.  

PSD3 doesn’t just tighten rules. It implicitly requires a different architecture, different tooling. 

Why Behavioural Intelligence Is Now Central, Not Optional 

The fraud typologies that PSD3 is most focused on, particularly APP fraud and account takeover, share a common characteristic: they’re hard to catch at the transaction level alone. A payment instruction may look entirely legitimate in isolation. The anomaly only becomes visible when you layer in behavioural context: Is this consistent with how this customer normally behaves? Is the session access pattern unusual? Is the same device and behavioural pattern spotted across other accounts and payment methods?  Has the beneficiary relationship changed recently? 

This shift explains why the industry has been moving toward a more integrated approach to fraud prevention. To comply with PSD3 and evolving fraud, institutions shall combine entity-level risk profiling, session-level intelligence, and transaction-level risk scoring to create a fuller view of risk before a payment is executed. 

The challenge is that, in most institutions, these capabilities remain siloed. Behavioural analytics may sit in a separate system or be missing altogether, while transaction monitoring is split across channels, with one solution for cards and another for wire transfers. This often leaves instant payments, account-to-account payments, crypto payments, and buy-now-pay-later flows insufficiently covered, especially when detection and decisioning must happen within milliseconds. 

The result is a fragmented control environment, with no unified decision point that brings all relevant signals together before a payment is released. 

The gap between these layers is where fraud increasingly lives. Schemes evolve precisely to exploit the seams between detection systems. Static rules, however sophisticated, are inherently reactive, they catch what’s already been seen. The more durable approach combines rules-based detection for known patterns with unsupervised machine learning that identifies deviations from normal behaviour without requiring prior fraud examples. This handles both the known unknowns and the genuinely novel. 

The Swift Dimension That Often Gets Overlooked 

Much of the conversation around PSD3 and instant payments focuses on domestic retail rails, which makes sense given where consumer fraud volumes are concentrated. But high-value cross-border payments represent a distinct and underserved risk surface. 

Swift traffic sits largely outside the scope of consumer-focused fraud tools. Yet correspondent banking flows carry significant value, and the attack vectors, compromised operator credentials, fraudulent payment instructions, manipulation of debit confirmations, are well-documented. The ability to monitor Swift messages at multiple interception points, cross-reference MT900 confirmations against MT103 instructions, and, critically, issue stop-and-recall instructions via the GPI tracker for payments already in-network, meaningfully extends the intervention window beyond what’s possible on domestic rails. 

Very few fraud prevention architectures address this channel natively alongside retail payments. That gap deserves more attention as institutions think about end-to-end coverage. 

From Compliance Burden to Architecture Decision 

The institutions that will navigate PSD3 most effectively aren’t those that treat it as a compliance checkbox. They’re the ones that use the regulatory moment to reassess their fraud prevention architecture more fundamentally, asking not just “what do we need to do to comply?” but “what does a genuinely real-time, multi-channel fraud prevention capability actually look like, and do we have it?” 

That question tends to surface uncomfortable answers. Fragmented point solutions. Offline analysis loops. Gaps in channel coverage. Detection capabilities that operate after execution rather than within it. Manual fraud investigation processes. Rapidly growing fraud volumes that institutions are expected to manage without proportionally increasing investigator teams and operational costs. 

The regulation provides the mandate. The harder work is architectural: building or acquiring a unified control layer that sits within the payment workflow, combines behavioural and transactional signals, covers the full range of payment rails, and makes preventive decisions in real time rather than purely detective ones after the fact. Done well, this approach can strengthen detection, improve the customer experience, reduce operational costs, and significantly increase the effectiveness and productivity of fraud investigators.  

That’s not a product category. It’s an infrastructure requirement. And PSD3 has just made it non-negotiable. 

Continue Reading

Business

The compliance cost trap and why efficiency must be the next frontier

Hassan Zebdeh, Financial Crime and Payment Advisor at Eastnets, outlines how banks can achieve stronger compliance outcomes by embracing more efficient, connected ways of working. 

Compliance has become one of the most resource-intensive functions inside modern banks. Year after year, institutions invest more people, more technology and more time into meeting expanding regulatory expectations, yet many find themselves no closer to achieving meaningful reductions in risk. Or cost. 

At the same time, financial crime is evolving daily, payments are moving in real time and regulators are increasingly focused on outcomes rather than process. While effort may increase, effectiveness doesn’t always follow suit. The systems and processes that once supported compliance in a pre-AI age are now being stretched to their limits, revealing a widening gap between what institutions put in and what they get back. 

This growing imbalance raises a critical question for the industry: how financially sustainable is the current approach to compliance, and what needs to change if banks are to keep pace with risk and regulation? 

The growing strain on compliance

Regulatory compliance can now account for more than 13% of operating costs, yet many banks continue to struggle with the same operational challenges. For most, rising spend has become the default setting for keeping up with regulatory obligations, rather than a reliable way to improve how risk is managed in practice. 

Part of the challenge lies in how compliance has evolved. In recent years alone, banks have had to absorb a wave of new and evolving requirements – from the EU’s AML Package and DORA’s operational obligations to global FATCA/CRS reporting deadlines and many other regulations globally. The response to these changes has often involved layering new controls, systems and processes onto existing ones, adding complexity without fundamentally rethinking how compliance has changed. 

The result is an environment that’s increasingly fragmented and difficult to scale. Compliance teams are expected to deliver faster detection, clearer auditability and stronger risk differentiation, while still relying on operating systems shaped by outdated processes and disconnected data. And yet, a single alert can take anywhere up to 22 hours to action – while some instant payments schemes require decisions in seconds, other nations still operate within minutes or longer. Sanctions lists are also changing, with the Office of Foreign Assets Control (OFAC) imposing sanctions on [https://”/]over 1,300 individuals and entities in 2025 alone, with this likely to double in 2026​. Banks are having to manage risk continuously, even as they attempt to modernise operations that were never designed for today’s pace, landscape or scale. 

Making matters harder, many firms are struggling to find and retain professionals with the right mix of legal, technical and operational expertise to work on these older platforms too. Experienced professionals are retiring en-masse, while nearly half of the new entrants lack the right experience needed to step into these roles effectively. Then again, why would the modern workforce want to work on outdated systems when they can choose new, more agile players within the industry? 

Taken together, this all culminates into a costly endeavour. There is little being done on a broader scale to address the underlying mismatch between rising complexity and operational capacity. Therefore, to keep pace with risk and regulation, we need an entirely different approach; one that focuses more on how compliance is designed, connected and executed. 

Reimagining compliance for a real-time world

For banks willing to rethink how compliance operates, this moment presents a clear opportunity to not only strengthen oversight, but to escape a cycle of rising cost and diminishing returns. As regulatory expectations rise and financial infrastructure accelerates, institutions have a chance to move beyond reactive expansion and build compliance frameworks that are both more effective and more economically sustainable. 

An efficiency-driven compliance framework is central to breaking this cycle. Rather than increasing headcount or layering new processes each time risk or regulation evolves, the focus needs to be on improving how compliance work is performed. By reducing duplication and allowing better decision-making at scale, efficiency helps banks contain costs while improving outcomes, addressing the root cause of the compliance cost trap. The question becomes; how can organisations unlock these improvements? In practice, this shift is anchored in four core capabilities that together redefine modern compliance. 

First, automation helps decouple compliance effectiveness from both headcount growth and large-scale system change. By streamlining the likes of data collection, enrichment and alert handling on top of existing environments, automation reduces manual effort without requiring a full ‘rip and replace’ approach of legacy platforms. This lowers the cost of day-to-day compliance activity while improving consistency and investigation speed. 

Next, risk-based approaches make sure resources are applied where they make the most difference. In practice, this means deeper scrutiny for higher-risk customers, geographies or transaction patterns, while allowing faster, lighter-touch processing for low-risk activity. With AI models and agents, banks can learn from historical patterns, detect subtle anomalies and adapt to evolving fraud and financial crime typologies, using a risk-based approach to automatically reduce false positives. But by tailoring controls to actual exposure, institutions can improve outcomes while reducing unnecessary operational burden. 

The third capability is streamlined reporting. This can be a time-consuming component of compliance, but automated, standardised reporting helps institutions meet regulatory obligations more efficiently, particularly across jurisdictions. By producing consistent, explainable and audit-ready outputs, financial institutions can reduce the recurring cost of manual reconciliation, remediation and regulatory engagement – all while strengthening compliance confidence. 

Finally, interoperability underpins efficiency. Compliance systems rarely operate in isolation and replacing them outright is too costly and disruptive. Interoperable environments, however, allow institutions to modernise incrementally – connecting existing systems, eliminating duplication and extending the value of current investments – without downtime or operational risk. 

Together, these four capabilities help shift compliance away from perpetual cost growth and toward a more stable, scalable model. Efficiency simply becomes the next frontier. Not as a shortcut, but as the mechanism through which banks strengthen defences, control costs and remain resilient in an increasingly demanding regulatory environment. 

Escaping the cost trap

As regulation becomes more outcome-focused and financial crime continues to evolve, banks are being pushed to reconsider not how much they spend on compliance, but how effectively that investment is put to work. 

Efficiency now represents the next frontier of compliance. And those institutions that rethink how compliance is designed, connected and scaled will be better positioned to strengthen defences, control cost growth and respond faster to change.  

The opportunity ahead is to move compliance beyond perpetual expansion and toward purposeful design. For banks, regulators and the wider financial ecosystem, the objective is clear: build compliance frameworks that are fit for the future, resilient by default and capable of keeping pace with risk – all without letting cost become the limiting factor. 

Continue Reading

Business

Why Resilience Is Replacing Prevention as the Defining Cybersecurity Strategy

by Manuel Sanchez, Information Security and Compliance Specialist, iManage

For decades, cybersecurity centered around prevention. Build the right walls around your perimeter, deploy the right tools, train your people not to click the wrong links, and you could keep the bad actors out.

Today, the question driving security strategy is no longer “how do we stop a breach?” but “how do we survive one?” It is a subtle but profound shift in philosophy, and it is reshaping everything from how IT and Security leaders structure their teams to how they select their vendors and deploy AI.

Rehearsing for the worst

The practical expression of this shift is visible in how security teams are being restructured. Organisations are establishing dedicated disaster recovery teams – not to prevent incidents, but to contain and recover from them when they occur. These teams maintain detailed, regularly updated playbooks covering everything from backup restoration to stakeholder communications, with roles pre-assigned and procedures rehearsed well in advance.

In many ways, this mirrors the logic behind disaster drills: fire alarms matter, but knowing the evacuation routes and the post-incident recovery plan determines how well an organisation survives. Critically, responsibility cannot rest with the CISO alone. Business continuity after a cyber incident is a whole-company challenge – which means every core part of the organisation is involved to sustain critical business operations.

Governance in the gray areas

Running alongside this shift is a governance crisis that is easy to underestimate until it becomes a serious risk. As organisations adopt more applications across more vendors and hosting services, the shared responsibility model that was supposed to keep cloud accountability clear has become increasingly difficult to enforce.

The sheer volume of cloud applications in use at any given enterprise is too vast for consistent governance under current approaches – and bad actors have become skilled at identifying exactly where vendor responsibility ends, and customer accountability begins, then operating precisely in that “gray area”. Being aware of this risk and putting preventative measures in place is important, but recognising the role these cloud applications play and the impact to key business operations if these applications were compromised, is critical.

Meanwhile, data volumes continue to grow exponentially, and unstructured data continues to accumulate in the background across many digital systems. Why is this important? If you don’t know what data you have, where it is stored, who has access to it, and, most importantly, how it is protected – onsite or cloud backup – this makes the recovery process a lot harder.

AI agents on the rise – and with it new risks

Although the focus of this article is on resilience, prevention must still remain an essential part of your defences. On that front, the accelerating adoption of autonomous AI in cyber defence tasks is reshaping security operations as visibly as anything else happening in the field right now. The volume, speed, and sophistication of modern threats have simply outpaced what human analysts can manage in real time.

The shift is toward AI that doesn’t just flag anomalies for human review, but actively detects, analyses, and neutralises threats as they emerge, even using predictive models to anticipate attacks before they fully materialise. This frees human experts to focus on strategic decisions and complex defence work rather than spending their days firefighting.

Autonomous AI does, however, introduce risks of its own. When AI agents operate across systems – accessing sensitive repositories, triggering actions, sharing data – they expand the attack surface in ways that aren’t always immediately visible.

Managing the digital identities of AI agents, much like managing employee access credentials, is becoming a critical security discipline. Accordingly, comprehensive traceability frameworks that log every action an agent takes are no longer optional; they are the foundation of responsible AI deployment in any security context.

The supply chain wake-up call

The case for moving from a “prevention” mindset to a “resilience” one is further bolstered by recent high-profile breaches via compromised managed service providers, which have forced a fundamental reset in how organisations evaluate their vendors.

The era of cost-first selection is over. Security credentials, demonstrated through continuous and verifiable evidence, are now non-negotiable for any provider hoping to retain enterprise clients – and what organisations are demanding goes well beyond point-in-time audits. They want real-time visibility into every third-party integration, every software update, and every vendor interaction – including the cloud services the vendors themselves use.

“Trust but verify” has become the operational standard, and providers who cannot demonstrate validated controls and live monitoring are finding themselves out of contention. It is a structural shift that will reshape the vendor landscape considerably — and it is already underway.

A new era demands a new approach

In the end, prevention still matters, but resilience – instilled via the key focus areas above – is what turns disruption into survivable events rather than existential crises. The organisations that are honest about the limits of prevention and embrace the shift towards resilience won’t just better withstand the next wave of attacks – they’ll be differentiating themselves from competitors still clinging to yesterday’s playbook.

Continue Reading

Copyright © 2026 Futures Parity. | Designed and Developed by 18arts Studio